

| File Reference : | GG-8-05 Secure Project Management and Outsourcing |
| Date File Updated | 07-10-26 |
| Category | General Guidance | Tags: ISO 27001, 4.2, 4.3, 6.1, 7.1, 7.2, 7.3, 8.1, IMS1 8.2, IMS1 8.3 |
Included in the alphaZ subscription
Every alphaZ document and toolkit, with updates as they are released. Everything you download is yours to keep.
You are logged in as an alphaZ subscriber
This document's file is ready to download from the Download Files tab below.
This guidance shows how to build information security into project plans and supplier choices, with the review points, outsourcing risks and controls to use.
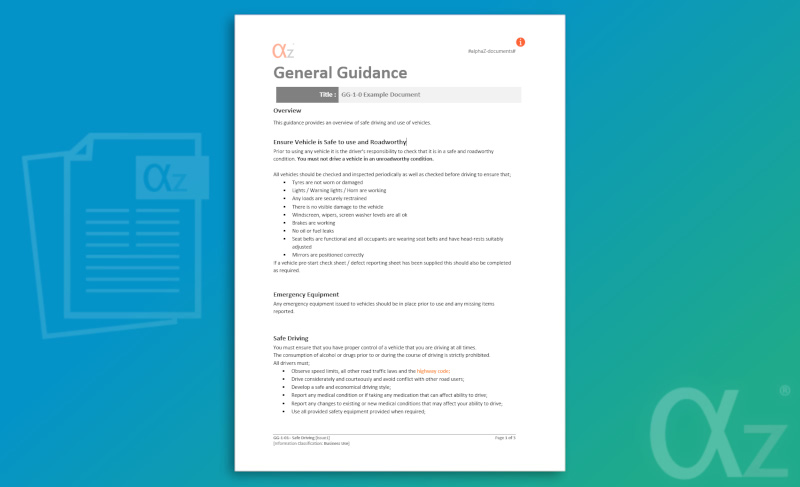
This guidance document is supplied in fully editable MS Word format and can be easily customised and edited. The document uses pre-defined style formatting throughout, with all text in Calibri font for improved readability.
The following document labelling is included in the footer:
- Guidance number and title
- Information-classification
- Version
- Page number / total pages

Further guidance on supplier and project information security:
These files are included in the alphaZ subscription. The training talk is also included in the ISO 27001 and ISO 22301 toolkits, including the integrated toolkits that combine them.

If you'd like hands-on help building information security into your projects and supplier checks, our remote support services provide direct expert input from our team, by the day, by project, or on an ongoing basis.

Secure Project Management and Outsourcing Guidance
A general guidance document on secure project management and outsourcing, for anyone who manages projects or selects and manages suppliers. It explains why information security belongs in every project plan, what to consider when reviewing it, the information security risks of outsourcing, and the controls that reduce them.
Topics Covered
- Projects and information security - what a project is, and why information security is part of every project plan whatever its size
- Why it matters - examples of what happens when information security is left out of a project plan or supplier selection
- Building it into projects - adding information security to the development procedure and project planning templates, and training everyone who manages projects
- Reviewing a project - the points to consider, from information classification, access, transfer and storage to whether a data protection impact assessment is needed
- Risks of outsourcing - suppliers unaware of the company's requirements or their own obligations, lacking controls, leaking information or working without a contract
- Controls when outsourcing - checked suppliers, sharing the relevant policies, non-disclosure agreements, binding contracts where risk is high, and supplier audits
Who Is It For?
Anyone who plans or manages projects, and anyone involved in selecting, contracting or managing suppliers and service providers.
Included in the ISO 27001 and ISO 22301 Toolkits
This guidance is supplied with the TT-8-05 Secure Project Management and Outsourcing training talk, which is part of the ISO 27001 and ISO 22301 toolkits, including the integrated toolkits that combine them.
Using the Guidance
Issue it to project managers and staff who deal with suppliers, go through it with the matching training talk, and keep it as a reference when a project or outsourcing arrangement starts. Record who has received it, for example on the training matrix.
When Security Is Left Out
Short examples show the impact when information security is missed. In one, a client database is hacked through a vulnerability nobody considered and personal information is leaked. In another, a supplier chosen without checking its information security controls lets critical company information reach competitors. Each makes the case for considering information security from the start.
Adapting the Guidance
Edit the guidance to match your own arrangements - your development procedure and project planning template, how suppliers are checked and approved, and the agreements and contracts you use with suppliers.
Related Documents
Other documents that work alongside this guidance:
- PP-8-08 Secure Development Policy Procedure
- PP-8-11 Information Technology Outsourcing Policy Procedure
- PP-8-12 Information Classification and Protection Policy Procedure
- P-37 Supplier Security Policy
- F-Q21 Data Transfer and Processing Agreement
- F-Q97 Data Protection Impact Assessment
- GG-8-06 Information Transfer
Would you rather we prepared it for you?
A day of remote support can build your information security risk register around your actual systems - your risks scored with a named owner, the treatment decided for each one and the Annex A controls that apply - so the controls your staff are briefed on are the ones you have chosen.
These files are for alphaZ subscribers. Log in to the subscriber library once and each file below downloads straight away. Not a subscriber yet? See the alphaZ subscription.
Each file downloads straight away. You can also browse the subscriber library.


