

| File Reference : | P-93 Personal Data Subject Access Request Policy |
| Date File Updated | 05-10-26 |
| Category | Policies | Tags: ISO 27001, UK GDPR, subject access request, SAR, data subject rights |
Included in the alphaZ subscription
Every alphaZ document and toolkit, with updates as they are released. Everything you download is yours to keep.
You are logged in as an alphaZ subscriber
This document's file is ready to download from the Download Files tab below.
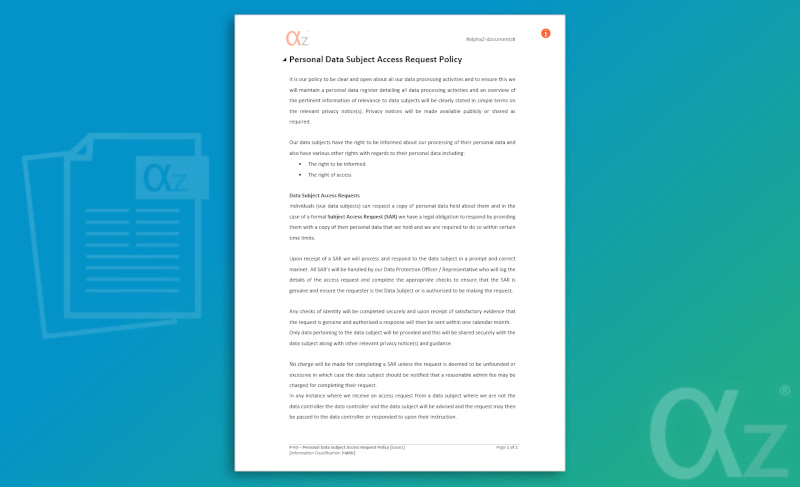
A personal data request policy template that explains how to make a request for access and for each of the other rights, and what happens next.
This policy template is supplied in fully editable MS Word format and can be easily customised and edited. The document uses pre-defined style formatting throughout, with all text in Calibri font for improved readability.
The following document labelling is included in the footer:
- Policy number and title
- Information-classification
- Version
- Page number / total pages

Further guidance on data protection rights:

Download this policy template with your company name and logo already added!
Document Preparation is included with the alphaZ subscription.
This file is included in the alphaZ subscription. This policy is also included in the GDPR / Data Protection Toolkit and the ISO 27001 toolkit and the integrated toolkits that include it, so the toolkit route gives you this file plus everything else you need in one download.

If you'd like this policy prepared for your organisation along with the rest of your company policies, or help preparing your personal data register and privacy notices, our remote support services provide direct expert input from our team, by the day, by project, or on an ongoing basis.

Subject Access Request Policy Template
A public policy for explaining how your organisation handles requests from people about their personal data. It covers requests for a copy of personal data and the other rights - correction, erasure, restriction, portability, objection and rights relating to automated decisions - with how to make a request and what happens next.
What the Policy Covers
- Your rights - the rights people have over their personal data
- How to make a request - who to contact, the identity check and when the time limit starts
- Requests for a copy of your personal data - what is provided, including records held in AI tools, and when
- Other requests - how requests for the other rights are handled
- Where we are not the data controller - what happens when the organisation holds the data for someone else
- Complaints - how to raise a concern
An Optional Standalone Policy
The PP-1-16 Data Protection Policy Procedure already contains the subject access content in its section Transparency and Data Subject Access (Subject Access Request Policy), so a company using the procedure does not need this separate file. It is here for organisations that want a standalone, publicly shareable policy on this one subject - to give to a customer or answer a questionnaire, for example. Where both are used, make sure the policy says the same as the procedure.
Who Needs a Subject Access Request Policy?
Any organisation that wants a standalone document explaining request handling - to publish, to give to someone who has asked for their data, or to evidence the process to a customer.
Included in the GDPR / Data Protection Toolkit
This policy is part of the GDPR / Data Protection Toolkit - the registers, forms, policies, procedure and guidance for documenting how you collect and process personal data, in one download, and is also included in the ISO 27001 toolkit.
Works with the Subject Access Request Form
Each request is logged and worked through on the F-Q73 Subject Access Request, which records the type of request, the identity check, the response due date, any extension and what was provided.
Using the Policy
Add your company details and approval, and insert the postal and email address people should use to make a request where the yellow prompt shows. Publish the policy or give it to anyone who asks how to make a request.
Records Held in AI Tools
Personal data held in AI tools - prompts, outputs, meeting transcripts and chatbot conversations - is included when a copy of personal data is requested. The policy says so, so searches for a request cover those records too.
Timescales
The policy explains when the time limit starts, the normal response time, and when and how an extension is applied and communicated.
Related Documents
Other documents in the GDPR / Data Protection Toolkit that work alongside this one:
Would you rather we prepared it for you?
Our Personal Data Register and Privacy Notice Preparation service works through the personal data your organisation holds with you, including the AI tools in use, and prepares the register and privacy notice so they describe what actually happens to that data.
These files are for alphaZ subscribers. Log in to the subscriber library once and each file below downloads straight away. Not a subscriber yet? See the alphaZ subscription.
Each file downloads straight away. You can also browse the subscriber library.
- P-93 Personal Data Subject Access Request Policy Word, 32 KB


