



| File Reference : | A-C Management System Cyber Security |
| Date File Updated | 23-09-2025 |
| Category | Management System Checklists | Tags: ISO 27001 |
Included in the alphaZ subscription
Every alphaZ document and toolkit, with updates as they are released. Everything you download is yours to keep.
You are logged in as an alphaZ subscriber
This document's file is ready to download from the Download Files tab below.
This checklist audits cyber security arrangements, from policies and controls to malware protection, phishing awareness and incident response.
Prepared using the F-Q2 Audit Checklist form template.
The file is supplied in fully editable MS Word format and can be easily customised, with all text in Calibri font for improved readability.
The following document labelling is included in the footer:
- Checklist number and title
- Information-classification
- Version
- Page number / total pages

Further guidance on cyber security and internal auditing:

Download this audit checklist template with your company name and logo already added!
Document Preparation is included with the alphaZ subscription.
This file is included in the alphaZ subscription.

If you'd like hands-on help completing your internal audits or training your internal auditors, our remote support services provide direct expert input from our team, by the day, by project, or on an ongoing basis.

Cyber Security Audit Checklist Template
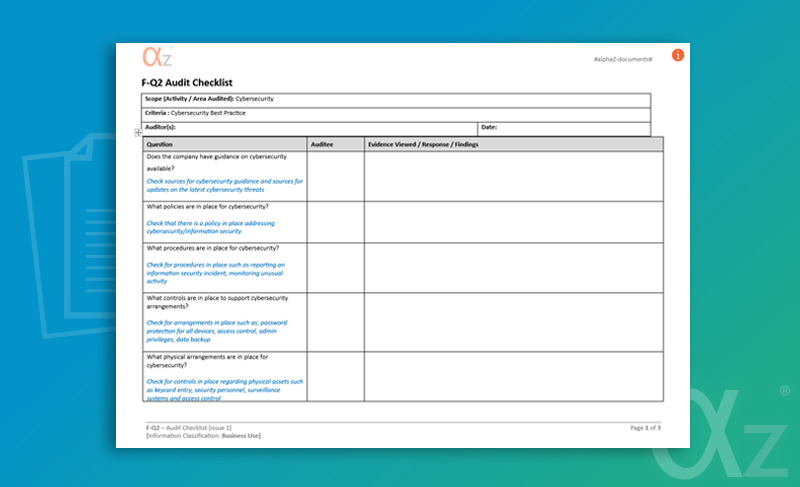
A management system audit checklist for cyber security, set against good practice rather than a single standard, with a note under each question on what to check. It is set out on the F-Q2 Audit Checklist format, with the scope, criteria, auditor and date recorded at the top, and each question alongside the auditee and the evidence viewed, response and findings.
Questions Covered
- Whether cyber security guidance is available, and where updates on the latest threats come from
- What policies and procedures are in place for cyber security, such as incident reporting and monitoring unusual activity
- What controls support the arrangements, such as password protection, access control, admin privileges and data backup
- What physical controls protect IT assets, such as key card entry, surveillance and access control
- How IT assets are tracked, issued and protected
- How information security risks for cyber security are identified and reduced
- How software and equipment are protected from malware, including anti-virus, updates, restrictions on downloads and USB devices, and firewalls
- Whether user accounts are set up on a least privilege basis
- What cyber security and phishing training staff receive
- Whether there is an incident response plan
- Whether the organisation works to the principles of confidentiality, integrity and availability
Carrying Out the Audit
The note under each question says what to look for, so the checklist can be followed by someone who is not an IT specialist. Ask to see the settings and records, such as the IT equipment register, the anti-virus status on a sample of devices and the user account rights, rather than relying on a description.
Planning the Audit
Have the information security policy, the IT equipment register, the information security risks register and the incident response plan to hand, and arrange time with whoever manages the IT systems. If IT is supported by an outside provider, ask them for the records beforehand.
Who Should Carry Out the Audit?
Anyone trained in internal auditing who is independent of the area being audited. The questions are written in plain language, so the checklist also works well for training new internal auditors.
Related Documents
Documents that work alongside this checklist:
- P-114 Cyber Security Policy
- ER10 IT Equipment Logins Register
- ER15 Information Security Risks
- PP-8-02 Anti Malware Policy Procedure
- F-Q109 Information Security Incident
Adapting the Checklist
The questions can be edited, added to or removed to suit the way the organisation works, and the scope and criteria at the top changed to match the area being audited. Because every alphaZ audit checklist uses the same F-Q2A layout, audit records look the same whichever area was audited, which makes them easier to review and compare.
Using the Findings
Weaknesses are raised as actions, prioritised by risk, and anything that leaves systems exposed is put right straight away.
Would you rather we did it for you?
Our Internal Audit Training and Support service works through your internal audits with you while training your own people as internal auditors, so the audits are completed and the skills stay in the business.
These files are for alphaZ subscribers. Log in to the subscriber library once and each file below downloads straight away. Not a subscriber yet? See the alphaZ subscription.
Each file downloads straight away. You can also browse the subscriber library.
- A C Management System Cyber Security Word, 51 KB


