

| File Reference : | ISO 27001:2022 Correlation |
| Date File Updated | Ref. toolkit |
| Category | ISO Correlations | Tags: ISO 27001 |
Included in the alphaZ subscription
Every alphaZ document and toolkit, with updates as they are released. Everything you download is yours to keep.
You are logged in as an alphaZ subscriber
This document's file is ready to download from the Download Files tab below.
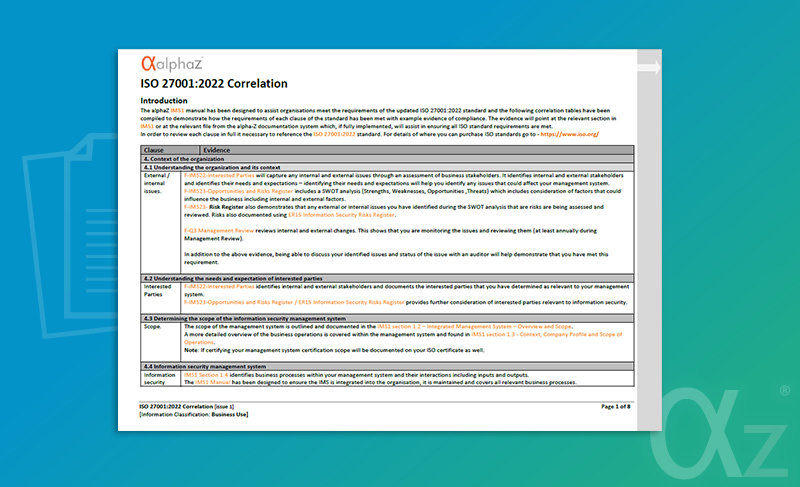
This correlation table maps each ISO 27001:2022 clause to where the evidence sits in the IMS1 manual and alphaZ information security documents, with an overview and guidance document for the standard.
These reference documents are supplied in PDF format within the alphaZ toolkits. They are for reference and are not intended to be edited.
alphaZ documents - tried and tested guidance documents. No junk, jargon or unnecessary content, developed over 25 years through practical use in the real world.
Further guidance on ISO 27001:
These documents are supplied within the alphaZ toolkits. They are included in the ISO 27001 toolkit and the integrated toolkits that include it.

If you'd like hands-on help preparing your information security risk assessment, treatment plan and Statement of Applicability, our remote support services provide direct expert input from our team, by the day, by project, or on an ongoing basis.

ISO 27001:2022 Correlation and Guidance
The ISO 27001:2022 Correlation and Guidance brings together a correlation table and an overview and guidance document for ISO 27001:2022. The correlation takes each clause of the standard, from Context of the Organisation to Improvement, and signposts the example evidence of compliance in the IMS1 manual and the alphaZ registers, forms and policies. The Annex A controls are covered by the separate Annex A correlation.
The alphaZ IMS framework follows how a business works rather than the clause order of the standard, so the correlation shows where each requirement is met. Use it when setting up the system, checking it or preparing for a certification audit.
Two Reference Documents
- ISO 27001:2022 Correlation - a clause by clause table giving each requirement and where the evidence sits in IMS1 and the alphaZ documents
- ISO 27001 Overview and Guidance - an introduction to the standard and its main requirements, with the points to have in place before a certification audit
What the Correlation Covers
- Clause 4 Context - issues, interested parties and scope, mapped to IMS1 Section 1 and the context and risk registers
- Clause 5 Leadership - commitment, the information security policy and roles, mapped to IMS1 Section 2
- Clause 6 Planning - risk assessment, risk treatment and the Statement of Applicability, mapped to IMS1 Section 8
- Clause 7 Support - resources, competence, awareness, communication and documented information
- Clause 8 Operation - carrying out risk assessments and risk treatment, mapped to IMS1 Sections 4 and 8
- Clauses 9 and 10 - monitoring, internal audit, management review, corrective action and improvement
Who Needs an ISO 27001:2022 Correlation?
The correlation is for organisations using the alphaZ IMS1 manual and documents with an ISO 27001:2022 information security management system. It helps IMS leads check each requirement is covered and find the evidence quickly for internal audits, management review and certification audits.
Included in the ISO 27001 Toolkit
These documents are part of the ISO 27001 toolkit and the integrated toolkits that include it.
Using the Correlation
Work through the table with IMS1 open, checking each evidence item is in place and reflects how you operate. The correlation is a PDF reference; for an editable clause by clause audit checklist use the ISO 27001:2022 Requirements Checklists.
Note: ISO clause checklists only include the clause numbers and short prompts for each clause (due to copyright reasons) and therefore a full version of the ISO standard is required to be used in conjunction with these checklists.
Related Documents
The correlation refers to documents such as the ER15 Information Security Risks Register, F-IMS26 Statement of Applicability, P-20 Information Security Policy, F-IMS22 Interested Parties Register, F-IMS23 Opportunities and Risks Register and ER2 Staff Training and Competency Matrix. The ISO 27001:2022 Annex A Correlation covers each Annex A control.
Would you rather we prepared it for you?
Our Information Security Risk and Treatment Plan service builds your information security risk assessment, treatment plan and Statement of Applicability around your real systems and data, checked by a consultant.
These files are for alphaZ subscribers. Log in to the subscriber library once and each file below downloads straight away. Not a subscriber yet? See the alphaZ subscription.
Each file downloads straight away. You can also browse the subscriber library.
- ISO27001-2022 Correlation PDF, 373 KB


