


| File Reference : | RA-BR8 Cyber Attack |
| Date File Updated | 22-06-2026 |
| Category | Business Risk Assessments | Tags: ISO 27001 |
Included in the alphaZ subscription
Every alphaZ document and toolkit, with updates as they are released. Everything you download is yours to keep.
You are logged in as an alphaZ subscriber
This document's file is ready to download from the Download Files tab below.
This is an example risk assessment covering the main cyber attack risks and the controls that manage them. It makes preparing your own much easier than starting from a blank page.

This example risk assessment has been prepared using the
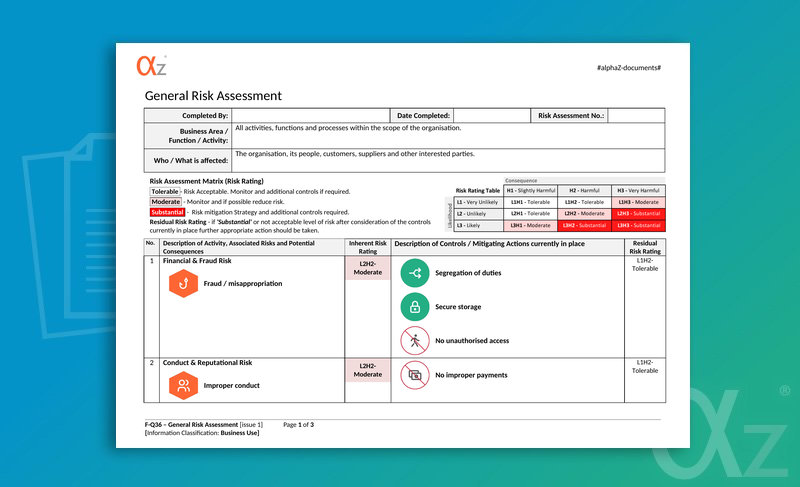
F-Q36 General Risk Assessment form template - a purpose-built template designed to focus entirely on what matters: identifying business risks, assessing their likelihood and impact, and recording the controls that manage them, without any unnecessary fields getting in the way.
The file is supplied in fully editable MS Word format and can be easily customised and saved to Google Docs format if required. The document uses pre-defined style formatting throughout with styles to match the risk-ratings which are input using select boxes pre-populated with all possible risk ratings. All text is in Calibri font for improved readability.
The following document labelling is included in the footer:
- Form number and title
- Information-classification
- Version
- Page number / total pages

Further guidance on cyber attacks and information security:

Download this form template with your company name and logo already added!
Document Preparation is included with the alphaZ subscription.
This file is included in the alphaZ subscription.

Cyber Attack Business Risk Assessment
This fully completed cyber attack business risk assessment example has been prepared by experienced ISO management system consultants. It covers the main forms of attack an organisation faces and how it prevents, detects, responds to and recovers from them, including phishing, malware and ransomware, hacking, denial-of-service, web application attacks and data breach. It can be used as a starting point when developing your own business risk assessment documentation.
What Does This Cyber Attack Business Risk Assessment Cover?
This risk assessment identifies the key cyber attack risks an organisation faces, including:
- Phishing and social engineering aimed at staff
- Malware and ransomware infection
- Hacking and unauthorised access to systems
- Denial-of-service attacks affecting availability
- Website and web application attacks
- Credential theft and account takeover
- Supply chain and third-party attacks
- Data breach and exfiltration
- Detection, response and recovery when prevention fails
A residual risk rating is then assigned to each risk, demonstrating how effective controls - such as staff awareness, multi-factor authentication, anti-malware and patching, network protection, monitoring and tested incident response - reduce the overall risk to a tolerable level.
A Professional Easy-to-Use Risk Assessment Template
This document uses colour-coded header styles matched to risk ratings, making it quick to read and easy to communicate during team briefings and staff training. A built-in risk rating matrix supports consistent evaluation of likelihood and consequence, and clear risk symbols help communicate each risk at a glance. An inherent and a residual rating are recorded for every risk, so the effect of your controls is easy to demonstrate.
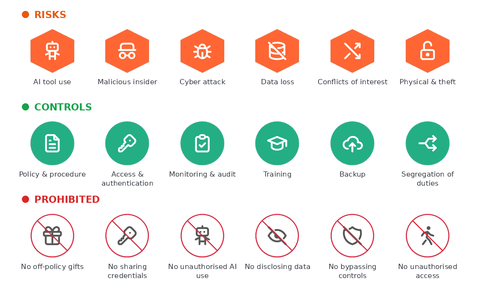
Risk, Control and Prohibition Symbols
Each row in the assessment is tagged with a small symbol so the type of risk, the control that manages it and any prohibition are clear at a glance. The same icon set runs across every alphaZ business risk assessment, which keeps a finished document quick to read and easy to compare. You can read more about them in our blog post on the alphaZ business risk icons.
Who Is This Cyber Attack Business Risk Assessment Template Suitable For?
This template is suitable for organisations of any size that need to identify, assess and document the risk of cyber attack. It is particularly useful when implementing or maintaining an information security management system aligned with ISO 27001, and when supporting the risks and opportunities requirements (clause 6.1) of ISO management system standards. Directors, IT and security leads and management system managers can all use it as a practical, ready-made starting point.
These files are for alphaZ subscribers. Log in to the subscriber library once and each file below downloads straight away. Not a subscriber yet? See the alphaZ subscription.
Each file downloads straight away. You can also browse the subscriber library.
- RA-BR8 Cyber Attack Risk Assessment Word, 195 KB


